
Why Every Organization Needs a Cybersecurity Roadmap
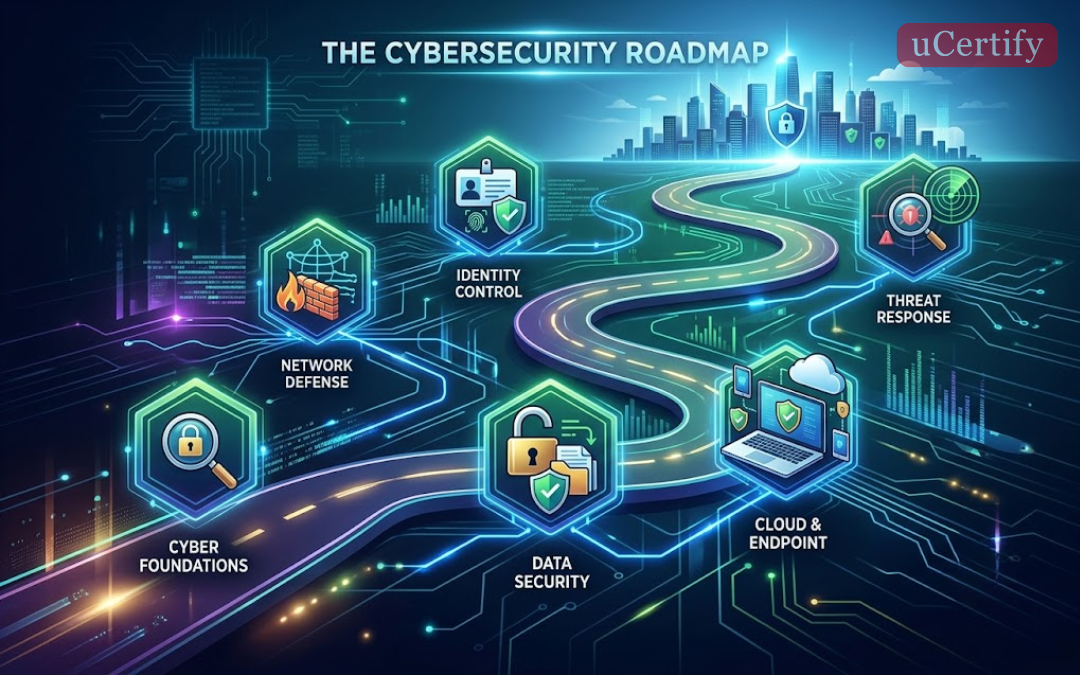
Cybersecurity is no longer limited to installing antivirus software or creating strong passwords. Modern businesses depend on cloud platforms, digital applications, remote work systems, and connected devices, which increases their exposure to cyber risks. A single security incident can interrupt operations, damage customer trust, and create financial losses. This is why organizations need a structured Cybersecurity Roadmap that defines where they currently stand, where they need to go, and how they will achieve stronger protection.
A Cybersecurity Roadmap acts as a long-term security strategy that connects business objectives with cybersecurity improvements. Instead of reacting to attacks after they happen, organizations can identify weaknesses, prioritize risks, and implement security controls before threats become serious incidents.
For example, a growing healthcare company may discover during a security review that patient information is stored across multiple systems without consistent access controls. A roadmap helps the company create a planned approach by improving identity management, implementing encryption, training employees, and meeting compliance requirements.
A successful roadmap is not just a technology plan. It combines people, processes, policies, and security solutions to create a complete defense strategy.
Understanding the Foundation of a Cybersecurity Roadmap
A strong Cybersecurity Roadmap begins with understanding the organization’s current security maturity. Before purchasing new security tools, businesses must evaluate their existing protection level, identify weaknesses, and understand their risk exposure.
The first step is a cybersecurity assessment that examines:
- Network infrastructure
- Cloud environments
- User access permissions
- Data storage practices
- Security policies
- Employee awareness levels
- Incident response capabilities
This assessment creates a security baseline. Without knowing the current position, organizations cannot create realistic security goals.
Many businesses make the mistake of investing heavily in security products without understanding their actual risks. For example, implementing an advanced monitoring system will not solve security problems if employees still use weak passwords or sensitive data is accessible to unnecessary users.
A roadmap ensures that security investments are aligned with business requirements rather than based only on technology trends.
Using Cybersecurity Frameworks to Create a Strategic Approach
Professional cybersecurity programs often use recognized frameworks to organize security activities. Frameworks provide structured guidance and help organizations avoid missing important security areas.
The NIST Cybersecurity Framework (CSF) is one of the widely used models that organizes cybersecurity activities into five core functions:
Identify
Organizations must understand their valuable assets, potential risks, and security responsibilities. This includes identifying critical systems, sensitive data, and possible vulnerabilities.
Protect
The protection stage focuses on implementing controls such as:
- Multi-factor authentication
- Data encryption
- Access management
- Security policies
- Employee training
Detect
Businesses need the ability to recognize suspicious activities quickly through:
- Security monitoring
- Threat detection tools
- Log analysis
- Vulnerability scanning
Respond
A response strategy defines how teams handle security incidents, communicate during emergencies, and limit damage.
Recover
Recovery planning ensures business operations can return quickly after an attack through backups, disaster recovery procedures, and system restoration plans.
Aligning a Cybersecurity Roadmap with security frameworks helps organizations create a more complete and measurable strategy.
Developing a Cybersecurity Implementation Plan
A Cybersecurity Implementation Plan converts security goals into practical actions. While the roadmap explains the direction, the implementation plan defines the specific steps required to achieve those objectives.
A well-designed implementation plan should include:
Security Priorities
Organizations should focus first on high-impact risks. Protecting critical business systems and sensitive information should receive priority over less important improvements.
Implementation Timeline
Security improvements should be divided into phases.
Example:
First 30 Days:
- Conduct vulnerability assessment
- Review user permissions
- Identify critical assets
- Update security policies
60–90 Days:
- Implement multi-factor authentication
- Improve network monitoring
- Begin employee security training
3–12 Months:
- Deploy advanced security monitoring
- Conduct penetration testing
- Improve compliance processes
Responsible Teams
Every security activity should have ownership. Assigning responsibilities ensures tasks are completed and progress can be measured.
Success Metrics
Organizations should track:
- Number of vulnerabilities resolved
- Security training completion rates
- Incident response time
- Patch management performance
- Compliance improvement
A measurable implementation plan transforms cybersecurity from an abstract goal into an operational process.
Network Security Best Practices for Reducing Cyber Threats
Network security remains one of the most important components of a Cybersecurity Roadmap because networks connect users, applications, and business systems.
Following Network Security Best Practices helps organizations reduce unauthorized access and limit potential damage from cyberattacks.
Important practices include:
Network Segmentation
Instead of allowing all systems to communicate freely, organizations should separate critical environments. If attackers compromise one area, segmentation reduces their ability to move throughout the network.
For example, a financial organization may separate customer databases, employee systems, and payment processing environments to reduce risk.
Strong Access Controls
Businesses should follow the principle of least privilege, meaning users receive only the access required for their responsibilities.
Regular Vulnerability Management
Security teams should continuously identify and fix weaknesses through:
- Security updates
- Vulnerability scans
- Configuration reviews
- Penetration testing
Secure Remote Access
With remote work becoming common, organizations must protect external connections through:
- Virtual private networks
- Multi-factor authentication
- Device security controls
Network security is not a one-time activity. It requires continuous monitoring and improvement.
Creating a Cyber Risk Management Strategy
Every organization faces cybersecurity risks, but not every risk requires the same level of attention. A Cyber Risk Management Strategy helps businesses identify which threats could cause the greatest impact and how resources should be allocated.
A practical risk management process includes:
Risk Identification
Organizations identify possible threats such as:
- Phishing attacks
- Malware infections
- Insider threats
- Data breaches
- Software vulnerabilities
Risk Analysis
Security teams evaluate:
- Probability of occurrence
- Potential business impact
- Existing protection measures
Risk Treatment
Companies can respond through four approaches:
- Reduce the risk through security controls
- Transfer risk through insurance
- Avoid unnecessary risks
- Accept low-impact risks
A mature risk strategy helps businesses make cybersecurity decisions based on evidence rather than assumptions.
Building Security Culture Through Cybersecurity Awareness Training
Technology cannot eliminate every cybersecurity risk because human behavior remains a major factor in security incidents.
Cybersecurity Awareness Training helps employees recognize threats and understand their role in protecting company information.
Effective training programs should cover:
- Phishing detection
- Password security
- Safe internet usage
- Data handling procedures
- Reporting suspicious activities
For example, an employee who understands how phishing works is more likely to identify a fake login email before entering company credentials.
Organizations should avoid treating training as a yearly compliance requirement. Security awareness should become an ongoing process through:
- Regular workshops
- Simulated phishing exercises
- Security newsletters
- Department-specific training
A security-aware workforce creates an additional protection layer against cyber threats.
Building a Data Protection and Compliance Roadmap
Data is one of the most valuable assets for modern organizations. A Data Protection and Compliance Roadmap ensures sensitive information is managed securely while meeting legal and industry requirements.
A strong data protection strategy includes:
Data Classification
Organizations should identify different categories of information:
- Public data
- Internal business data
- Confidential information
- Highly sensitive customer records
Encryption and Access Management
Sensitive information should be protected through encryption and controlled access policies.
Compliance Management
Businesses must understand regulations relevant to their industry, such as privacy and security requirements.
Compliance is not only about avoiding penalties. It also demonstrates responsible data management and builds customer confidence.
Implementing Modern Security Technologies
Technology plays an important role in strengthening cybersecurity defenses, but tools should support a broader strategy rather than replace proper planning.
Modern organizations often use:
Endpoint Security
Protects laptops, servers, and employee devices from malware and unauthorized activity.
Security Monitoring Platforms
Solutions such as SIEM systems help collect security data and identify suspicious behavior.
Zero Trust Security Model
Zero Trust follows the principle:
“Never trust automatically; always verify.”
Instead of assuming users or devices are safe because they are inside the network, every access request is continuously verified.
Cloud Security Controls
As businesses move workloads to cloud platforms, security strategies must include:
- Identity protection
- Cloud configuration monitoring
- Data security controls
Technology investments should always be connected to identified risks and business priorities.
Preparing an Incident Response and Recovery Strategy
Even organizations with strong security controls must prepare for possible incidents.
An incident response strategy defines how teams react when attacks occur.
A complete response process includes:
Detection
Identify unusual activities quickly.
Containment
Limit the spread of the attack.
Investigation
Determine what happened and which systems were affected.
Recovery
Restore normal operations safely.
Regular testing through simulations helps organizations identify weaknesses before a real emergency occurs.
For example, a ransomware simulation can reveal whether backup systems work correctly and whether employees understand their responsibilities during an attack.
Measuring and Improving Cybersecurity Performance
A Cybersecurity Roadmap should never remain unchanged. Threats, technologies, and business requirements constantly evolve.
Organizations should regularly review:
- Security performance
- Risk levels
- Compliance status
- Employee awareness
- Incident trends
Useful cybersecurity metrics include:
- Average time to detect threats
- Average time to recover from incidents
- Number of unresolved vulnerabilities
- Security training participation rate
Continuous improvement ensures that cybersecurity remains aligned with organizational growth.
Cybersecurity Roadmap Implementation Checklist
Organizations can use the following checklist as a starting point:
✓ Assess current cybersecurity maturity
✓ Identify critical assets and risks
✓ Create security priorities
✓ Develop a Cybersecurity Implementation Plan
✓ Improve network protection
✓ Establish a Cyber Risk Management Strategy
✓ Train employees regularly
✓ Protect sensitive information
✓ Monitor security performance
✓ Update the roadmap continuously
Conclusion: Creating a Stronger Digital Future Through Cybersecurity Planning
A Cybersecurity Roadmap provides organizations with a structured approach to protecting digital assets, managing cyber risks, and preparing for future threats. Effective cybersecurity requires more than advanced tools; it requires strategic planning, employee awareness, strong processes, and continuous improvement.
By combining a Cybersecurity Implementation Plan with Network Security Best Practices, a Cyber Risk Management Strategy, Cybersecurity Awareness Training, and a Data Protection and Compliance Roadmap, businesses can build a security program that supports long-term growth.
Organizations that treat cybersecurity as an ongoing business priority will be better prepared to prevent attacks, protect valuable information, and maintain trust in an increasingly connected digital environment.


No Comments Yet
Be the first to share your thoughts on this post!