
Why Risk Management Matters More Than Ever
Every organization depends on technology to keep its operations running smoothly. Customer information, financial records, employee data, and business applications are now stored and managed through digital systems. While this transformation has improved efficiency, it has also expanded the opportunities for cybercriminals. A single ransomware attack, phishing campaign, or insider mistake can interrupt business operations, damage an organization’s reputation, and lead to significant financial losses. This is why Risk Management has become a strategic business function rather than simply an IT responsibility.
This guide is designed for business leaders, IT professionals, cybersecurity practitioners, and students who want to understand how the NIST Framework helps organizations identify, assess, and reduce cyber risks. By the end of this article, you will understand the fundamentals of Risk Management, the importance of NIST CSF Implementation, the Risk Assessment Process, the NIST RMF Steps, practical Cybersecurity Risk Mitigation strategies, and how these concepts fit within an Enterprise Risk Management Framework.
Understanding Risk Management Beyond Cybersecurity
Risk Management is the structured process of identifying potential threats, evaluating their impact on business objectives, and implementing appropriate controls to reduce their likelihood or consequences. Contrary to a common misconception, risk management is not about eliminating every possible risk. Doing so would often be too expensive or impractical. Instead, organizations aim to reduce risks to an acceptable level while balancing operational efficiency, business growth, and compliance requirements.
A useful way to understand this concept is by distinguishing three closely related terms. A threat is anything capable of causing harm, such as ransomware, insider misuse, or natural disasters. A vulnerability is a weakness that can be exploited, such as outdated software or weak passwords. Risk is the possibility that a threat will exploit a vulnerability and negatively affect the organization. Understanding these differences helps decision-makers prioritize security investments instead of applying the same controls to every situation.
What Is the NIST Cybersecurity Framework?
The National Institute of Standards and Technology (NIST) developed the Cybersecurity Framework (CSF) to provide organizations with a practical and flexible approach to managing cybersecurity risks. Instead of prescribing rigid technical controls, the framework encourages organizations to align cybersecurity activities with business objectives and risk tolerance. This flexibility explains why companies across healthcare, banking, manufacturing, education, and government sectors have adopted it.
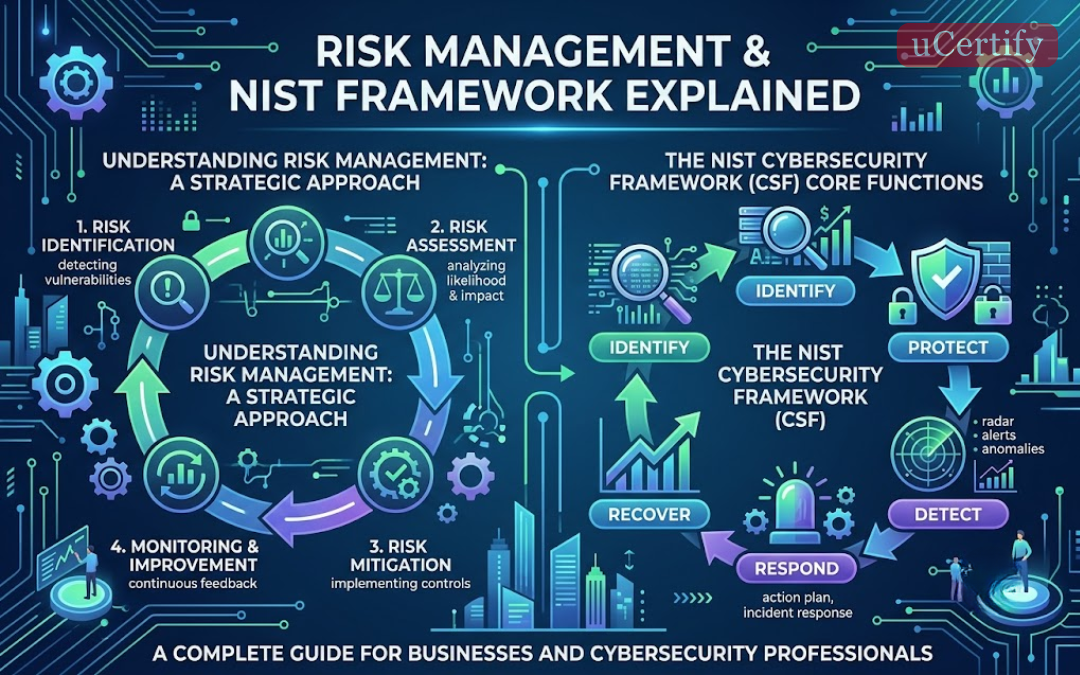
The framework is built around five core functions: Identify, Protect, Detect, Respond, and Recover. These functions create a continuous cycle rather than a one-time project. Organizations first identify critical assets and business processes before implementing protective measures. They then establish monitoring capabilities to detect suspicious activity, prepare response plans for security incidents, and develop recovery strategies to restore normal operations quickly. Together, these functions create a resilient cybersecurity program that evolves as new technologies and threats emerge.
Why NIST CSF Implementation Requires More Than Technology
Successful NIST CSF Implementation is not achieved by purchasing new security software alone. Many organizations invest heavily in technology while overlooking governance, employee awareness, and process improvement. As a result, expensive security tools often remain underutilized or misconfigured.
A practical implementation begins with assessing the organization’s current cybersecurity maturity. Security teams compare existing practices against the NIST Framework to identify capability gaps. Leadership then prioritizes improvements based on business impact rather than trying to solve every issue simultaneously. Departments such as IT, legal, compliance, human resources, and executive management should all participate because cybersecurity affects the entire organization, not just technical teams.
For example, a mid-sized healthcare provider may discover during implementation that patient records are encrypted, but employees have never received phishing awareness training. Rather than immediately purchasing additional software, the organization might first improve employee education and strengthen email security policies. This targeted approach often provides greater risk reduction at a lower cost.
Understanding the Risk Assessment Process Step by Step
An effective Risk Assessment Process provides organizations with a clear picture of their security priorities. Although every organization follows its own methodology, most assessments include several common stages.
The process begins by identifying valuable assets, including databases, cloud applications, customer information, financial systems, intellectual property, and operational technologies. Once these assets have been documented, security teams identify potential threats such as ransomware attacks, insider threats, supply chain compromises, phishing campaigns, and hardware failures.
The next step involves identifying vulnerabilities that could allow those threats to succeed. Examples include unsupported software, weak authentication practices, poor network segmentation, or inadequate employee training. Security professionals then evaluate both the likelihood of exploitation and the potential business impact if an incident occurs.
Consider a financial services company storing sensitive customer records in a cloud environment. If administrators discover that privileged accounts are protected only by passwords without multi-factor authentication, the likelihood of credential theft increases significantly. Because the data involved is highly sensitive, the overall risk rating becomes high. This assessment enables leadership to prioritize implementing stronger authentication controls before addressing lower-priority issues.
Regular risk assessments are equally important because business environments constantly evolve. Cloud adoption, mergers, remote work, regulatory updates, and emerging cyber threats continuously reshape an organization’s risk profile. Reviewing risks annually—or after major operational changes—helps organizations remain proactive instead of responding only after security incidents occur.
Exploring the NIST RMF Steps in Practice
The NIST RMF Steps provide a structured lifecycle for integrating cybersecurity risk management into organizational operations. Rather than treating security as a one-time compliance exercise, the Risk Management Framework promotes continuous improvement.
The first step prepares the organization by establishing governance, defining responsibilities, and understanding business objectives. Information systems are then categorized according to the sensitivity of the data they process, helping determine the level of protection required. Appropriate security controls are selected based on organizational requirements and regulatory obligations before being implemented across systems and applications.
After implementation, security professionals assess whether the controls function as intended. Leadership then reviews assessment results before authorizing systems for operational use. However, authorization does not mark the end of the process. Continuous monitoring remains essential because vulnerabilities, technologies, and attacker techniques change regularly. Routine vulnerability scanning, penetration testing, configuration reviews, and security audits help ensure controls remain effective over time.
Organizations that follow these structured steps often gain better visibility into their cybersecurity posture while making more informed investment decisions and demonstrating compliance with industry standards.
Practical Cybersecurity Risk Mitigation Strategies
Implementing effective Cybersecurity Risk Mitigation requires balancing people, processes, and technology. Security solutions alone cannot eliminate cyber risks if employees lack awareness or organizational policies remain outdated.
Strong identity and access management should be a priority, ensuring employees receive only the permissions required for their responsibilities. Multi-factor authentication significantly reduces the risk of compromised credentials, while encryption protects sensitive information both in transit and at rest. Regular vulnerability scanning and timely software updates help eliminate known weaknesses before attackers can exploit them.
Employee awareness remains equally important. Many successful cyberattacks begin with phishing emails that trick users into revealing credentials or downloading malicious files. Organizations that conduct regular awareness training and simulated phishing exercises often reduce successful attacks because employees become better at recognizing suspicious activity.
Incident response planning is another essential mitigation strategy. Clearly defined responsibilities, communication procedures, and recovery plans enable organizations to respond quickly during security incidents. Tabletop exercises allow teams to practice responding to realistic scenarios before an actual attack occurs, reducing confusion and improving recovery times.
Integrating Cybersecurity into an Enterprise Risk Management Framework
A mature Enterprise Risk Management Framework recognizes that cybersecurity is only one part of a broader organizational strategy. Financial risks, legal obligations, operational disruptions, supply chain dependencies, and reputational concerns all influence business success. Managing these risks separately often leads to inconsistent decision-making and duplicated efforts.
An integrated framework encourages executives, department heads, and security professionals to evaluate risks collectively. Leadership defines the organization’s risk appetite, establishes governance policies, allocates resources, and monitors performance through measurable indicators. Security initiatives are then prioritized according to business objectives rather than isolated technical concerns.
For example, a manufacturing company planning to adopt Industrial Internet of Things (IIoT) technologies should evaluate not only cybersecurity risks but also production downtime, regulatory compliance, vendor reliability, and operational resilience. Viewing these factors together enables more balanced investment decisions and reduces the likelihood of unexpected business disruptions.
Common Mistakes Organizations Should Avoid
Many organizations struggle with Risk Management not because they lack security technologies but because they overlook fundamental practices. One common mistake is treating risk assessments as annual compliance exercises instead of continuous business activities. Another is assuming that purchasing advanced security tools automatically improves protection without investing in employee training or governance.
Organizations also frequently underestimate third-party risks. Vendors, cloud providers, and supply chain partners often have access to sensitive systems, making them attractive targets for attackers. Regular vendor assessments and contractual security requirements should therefore form part of any comprehensive risk management strategy.
Finally, organizations should avoid measuring cybersecurity success solely by the number of technologies deployed. Effective Risk Management is demonstrated through reduced business risk, improved resilience, faster incident response, and stronger organizational awareness.
Key Takeaways and Final Thoughts
Effective Risk Management enables organizations to make informed decisions instead of reacting to cyber incidents after they occur. The NIST Cybersecurity Framework provides a practical roadmap for aligning cybersecurity with business objectives, while NIST CSF Implementation helps organizations strengthen governance, identify capability gaps, and prioritize meaningful improvements. A structured Risk Assessment Process ensures critical risks receive attention first, the NIST RMF Steps establish continuous oversight, and proactive Cybersecurity Risk Mitigation reduces exposure to evolving threats. When these practices are integrated into an Enterprise Risk Management Framework, cybersecurity becomes a strategic business capability rather than simply a technical function.
The organizations that build long-term resilience are rarely those with the largest security budgets. More often, they are the ones that continuously assess their risks, learn from emerging threats, involve leadership in decision-making, and create a culture where security is everyone’s responsibility. By adopting this mindset and treating risk management as an ongoing business discipline, organizations can better protect their assets, maintain stakeholder trust, and confidently navigate an increasingly complex digital landscape.



No Comments Yet
Be the first to share your thoughts on this post!